Information Security Management
Information Security Management Organization Vision
Faced with the severe challenges posed by the weaponization of generative AI and geopolitical tensions in 2025, ASUS recognizes that operational stability is the cornerstone of sustainability. To address risks such as data breaches, operational disruptions, and critical human errors, we have established a comprehensive risk management system: internally, we deepen employees’ cybersecurity awareness, while externally, we strengthen multi-layered protection for critical infrastructure and the supply chain. ASUS is committed to elevating cybersecurity governance; our Taiwan operations have implemented ISO 27001 (Information Security Management), ISO 27701 (Privacy Information Management), ISO 27017 (Information Security Controls for Cloud Services), and ISO 27018 (Protection of PII in Public Clouds), with the same control measures enforced across our global operational sites. Regarding product risk control and brand protection, we have successfully mitigated over 32% of unnecessary risk false positives through the Common Vulnerabilities and Exposures (CVE®) framework, effectively safeguarding our brand’s technical reputation and consumer trust. Furthermore, ASUS continues to deepen its Secure Software Development Life Cycle (SSDLC) and expand cybersecurity training capacity for cross-departmental R&D personnel, thereby creating long-term business value characterized by high defensive resilience.
The Information Security Committee was established in May 2020 to formulate the ASUS Group Information Security Policy. In September 2021, the company appointed a Chief Information Security Officer (CISO) and established a dedicated information security unit—the Digital Security Center—to invest in the comprehensive planning and promotion of information and product security. With the vision of “Building Digital Resilience, Enhancing Brand Trust; Pursuing Excellence, Security Together,” group cybersecurity initiatives are overseen by the Chairman, with the CISO reporting annually to the Board of Directors on group cybersecurity risks and progress.
ASUS Information Security Commitment
- Risk management: Establish an information asset risk assessment mechanism to determine acceptable risk levels and ensure that information assets are adequately protected, continually improve the information security systems, and prevent damage from unauthorized access or operational negligence.
- Monitoring and responding to information security threat: Monitor and identify sources of cyber threats and respond accordingly, participate in international cyber defense to strengthen information sharing and enhance the Group's overall cybersecurity resilience.
- Information security incident management: Ensure that all information security incidents or suspected security vulnerabilities are reported, investigated, and handled according to the appropriate procedures.
- Business continuity management: Establish operational continuity management control principles to ensure that systems and business processes continue to operate without disruption, meet high availability requirements, or recover quickly to an acceptable operational level.
- Supply chain security management: Ensure that suppliers comply with the Group's information security policy and enter into the necessary confidentiality or information security agreements.
- Product security: Ensure strong security practices at every stage of product development, promote security-first culture, and deliver products that are both reliable and secure.
- Training: Establish clear information security responsibilities for all employees, and conduct information security awareness programs to cultivate a culture of cybersecurity.
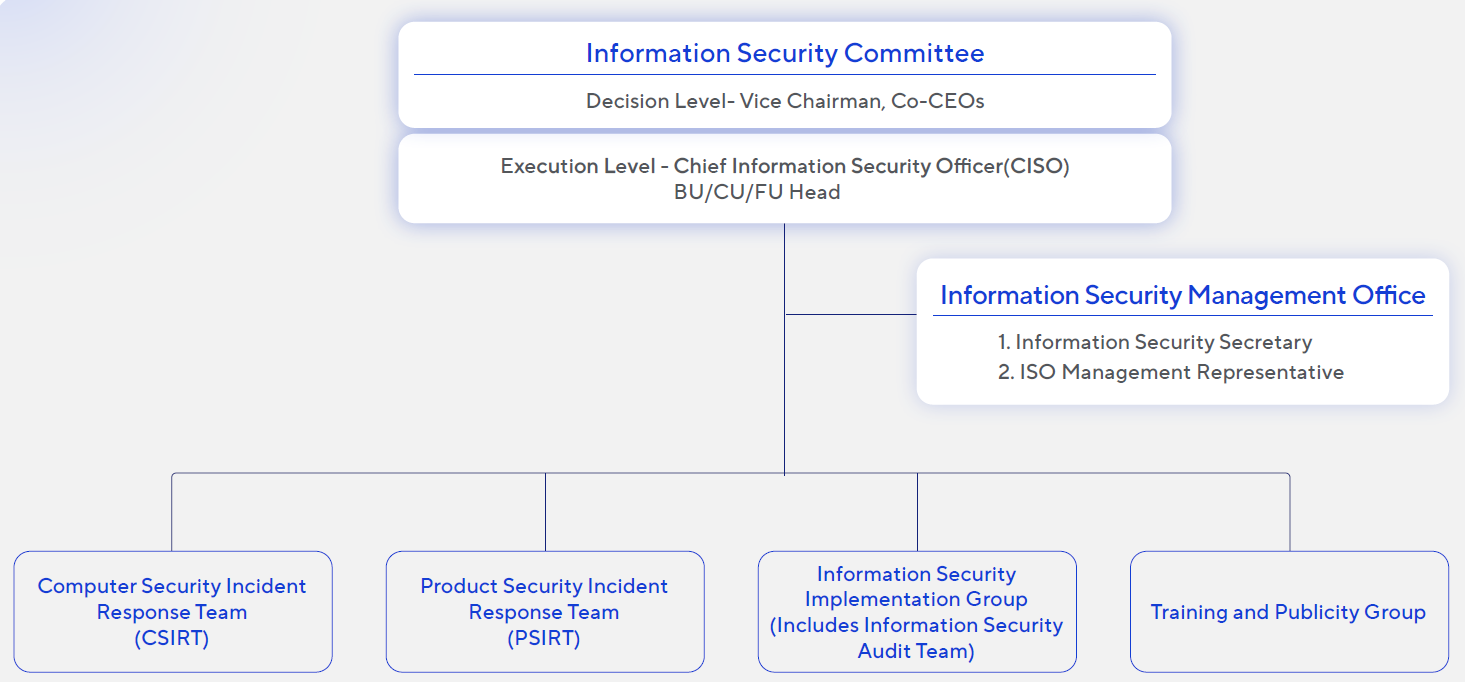
Four Major Management Domains of the ASUS Digital Security Center:
- Focus on information security management, risk assessment, and compliance issues within the organization and throughout the external supply chain.
- Real-time monitoring of internal and external information operation environment security threats and incident response actions.
- Promotion of product security engineering to enhance the information security of ASUS products and services.
- Assess configuration settings and architectural design risks for various cloud services or generative AI platforms and tools used by ASUS, and strengthen related security controls.
Four Main Action Themes and Policies
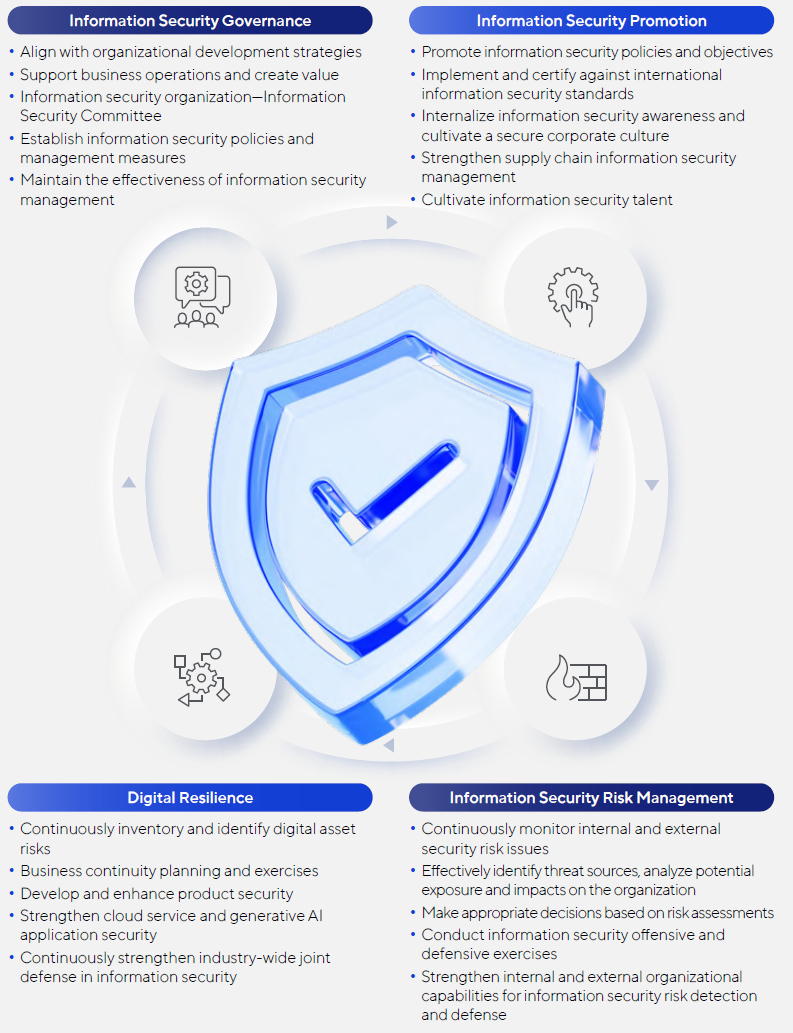
Information Security Management Performances in 2025

Information Security Governance
The Information Security Committee promotes the information security management system, establishing management procedures that align with international standards. We plan, execute, and review internal cybersecurity activities, verifying all activities and their related outcomes to ensure they meet the objectives of the information security management system.

Information Security Promotion
We conduct cybersecurity incident investigations, improvement, and response drills to assess the group’s cybersecurity defensive capabilities. We utilize the standards of the National Institute of Cyber Security (NICS) under the Executive Yuan as our drill targets, implementing social engineering drills to prevent business email compromise (BEC). We strengthen the advocacy of the ASUS Group Information Security Ten Rules and promote global cybersecurity general knowledge training for both incumbent and new employees, completing versions in 18 languages.
If employees discover any security incidents or operational issues (such as cybersecurity incidents, anomalies, system vulnerabilities, or any suspicious behavior), they shall follow the established reporting mechanism to escalate the matter step-by-step to supervisors or relevant departments. This ensures that issues are addressed and followed up on in a timely manner, aiming to mitigate corporate risks as early as possible.

Digital Resilience
In 2025, the ASUS Group undertook several key national projects, covering digital infrastructure for the government, AI and cloud platforms, and management systems for user and sensitive data. We leveraged the group’s cybersecurity capabilities to assist in the information security protection planning for these national-level projects, ensuring that vital national computing platforms meet the required protection levels for cybersecurity.

Risk Management
We monitor various digital security risks, assisting internal units in implementing and executing Business Continuity Plan (BCP) risk assessments, risk management, and crisis management plans. We also oversee the status of various drills to enhance the cybersecurity incident response and handling speed of our operations and monitoring teams.
In the new AI-driven era, ASUS is not only an observer of technology but also an active shaper. Through strategic governance, continuous learning, and cross-domain collaboration, ASUS continues to deepen the application and governance of generative AI and works with employees to build innovative, efficient, and forward-looking competitiveness. ASUS established the Generative AI (GenAI) Committee in 2024, demonstrating forward-looking thinking toward technological innovation. Under the strategic leadership of the Office of the CEO, ASUS built a cross-departmental governance mechanism that integrates resources from R&D, IT, cybersecurity, human resources, and legal functions. The committee transforms GenAI adoption from isolated technology introduction into a Group-wide strategic hub, comprehensively advancing the application and management of generative AI, empowering employees, and enhancing corporate competitiveness and innovation momentum.
Personal Data Protection Committee
To promote the protection and management of personal data for global consumers and ASUS employees, ASUS established the Personal Data Protection Committee (hereinafter referred to as PDPC ) in 2021. Internally, the “General Personal Data Protection Policy” serves as the guideline for the collection, processing, and use of personal information across ASUS products and services (e.g., computers, software, official websites, customer support, etc.). Externally, ASUS publishes a “Privacy Protection Policy ” on its website to inform the public and consumers about its data protection practices. For business partners involved in the collection, processing, or use of personal data, ASUS ensures compliance with data protection regulations through contractual agreements.
To ensure effective policy implementation, certain ASUS services obtained ISO 27701 Privacy Information Management and ISO 27018 Public Cloud Personal Data Protection certifications in 2023, and completed the group transition to the ISO 27001:2022 information security management standard in 2025, to reinforce systematic privacy management. The PDPC follows a risk management process that includes regular data inventory, improvement actions, periodic policy reviews and training, incident response and reporting, and annual internal audits. By the end of 2025, 410 regular PDPC meetings had been held.
PDPC Key Achievements in 2025

Data Inventory Review
Continue to examine the nature of data collected, processed and used by the company to ensure the scope of regulatory compliance.

Process Improvement
The Committee elaborates to the relevant departments on the data processing procedures that shall be modified and improved to be in accordance with personal data protection laws in response to the update of products or services.

Privacy Policy Review
Adjust the ASUS Privacy Policy for each country in response to regulations from different jurisdictions if needed.

Education and Training
In 2025, three training sessions were held for domestic and overseas employees, including annual cybersecurity awareness courses provided for all employees via in-person and online platforms.

Handle the Request and Inquiry of Data Subjects and Supervisory Authorities
The Committee is the central contact point for handling requests and inquiries of data subjects and supervisory authorities. ASUS shall respond to the requests from data subjects within the statutory period by law. The Committee collaborates with the relevant departments to handle requests and responds to the data subjects to fulfill the regulatory obligations. Inquiries from the supervisory authorities are also handled with the same approach to mitigate legal risks.

Annual Internal Audit
The responsible departments involved in the management of personal data are included in the scope of audit to cooperate the company's internal audit. With internal self assessment conducted by the departments, examination of service providers' practices conducted by the departments, and audits conducted by auditors, the Committee provides corrective measures and improvement approaches on non-compliant items to assist the responsible departments or service providers to improve their practices to ensure the full implementation of the company's policies and relevant management procedures.
New Regulatory Compliance Measures
In response to newly implemented data protection and online safety regulations in certain overseas countries, the committee collaborated with relevant departments to conduct data inventories and interviews, reviewed existing management and operational processes, and assisted in implementing compliant management mechanisms to ensure business operations align with legal requirements.
PDPC Key Plans in 2026
- Continue reviewing and improving compliance in response to changes in personal data regulations worldwide.
- Enhance data protection training and communications for domestic and overseas units to deepen understanding and compliance.