Risk Management
Risk Governance
In view of the increasingly complex risks faced by enterprises in their operations, which test the risk prevention capabilities and emergency response and recovery capabilities of enterprises, in order to enable the enterprise risk management mechanism to form good protection, identify possible future challenges, enterprises must take preventive measures early to avoid being affected, ensure that they are capable of dealing with threats and have the ability to continue operations, demonstrating organizational resilience.
Risk Management Policy
- Proactively deploy management measures in response to risk threats.
- Demonstrate organizational resilience and ensuring operational continuity.
 }})
Goals
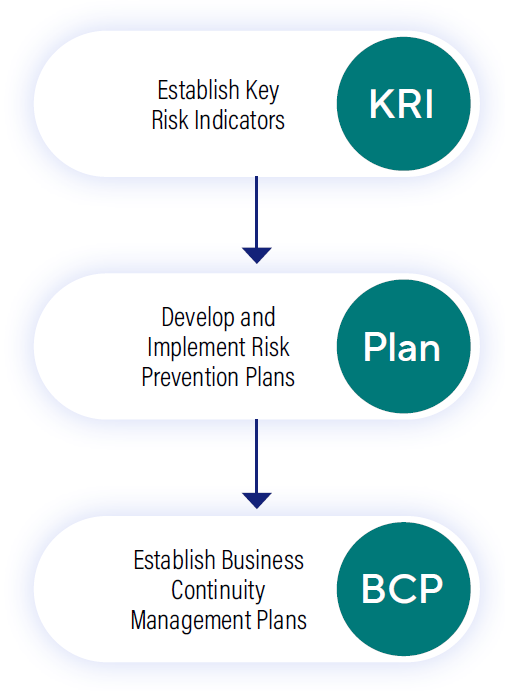
- Establish Key Risk Indicators (KRI) for real-time monitoring.
- Establish short, medium and long-term risk prevention plans,and review and improve them on a regular basis.
- Continuously strengthen various emergency response strategies and execute regularly drills
Business Continuity Management Committee
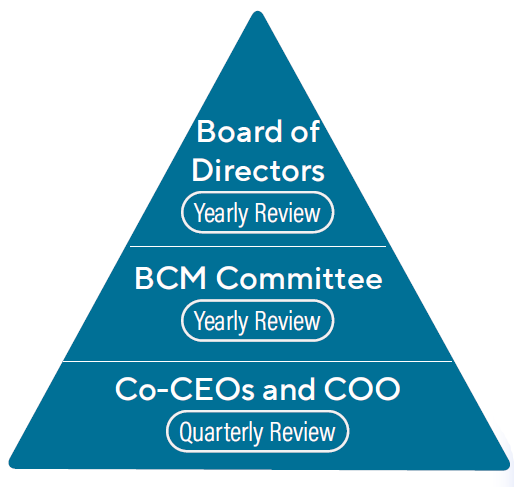
To ensure effective risk management, ASUS has established a Business Continuity Management (BCM) Committee, serving as a platform for communication between governance and operational units. ASUS also implements cross-departmental risk management mechanisms, breaking down departmental silos to transform risk response from reactive to proactive, thereby enhancing the Company's resilience against risks. In addition to establishing a regular review mechanism, ASUS adopts a three-line defense system to construct its internal control framework, and undergoes regular supervision at the board level.

| Organization | Role |
|---|---|
| Board of Directors | Oversees the strategy development of the BCM Committee |
| Business Continuity Management Committee | Oversee risk management operations |
| Business Continuity Management Office | Responsible for planning and supervising risk management and compliance across departments, as well as facilitating cross-departmental communication |
| Taskforce Units (TUs) | Responsible for identifying risks and implementing mitigation measures |
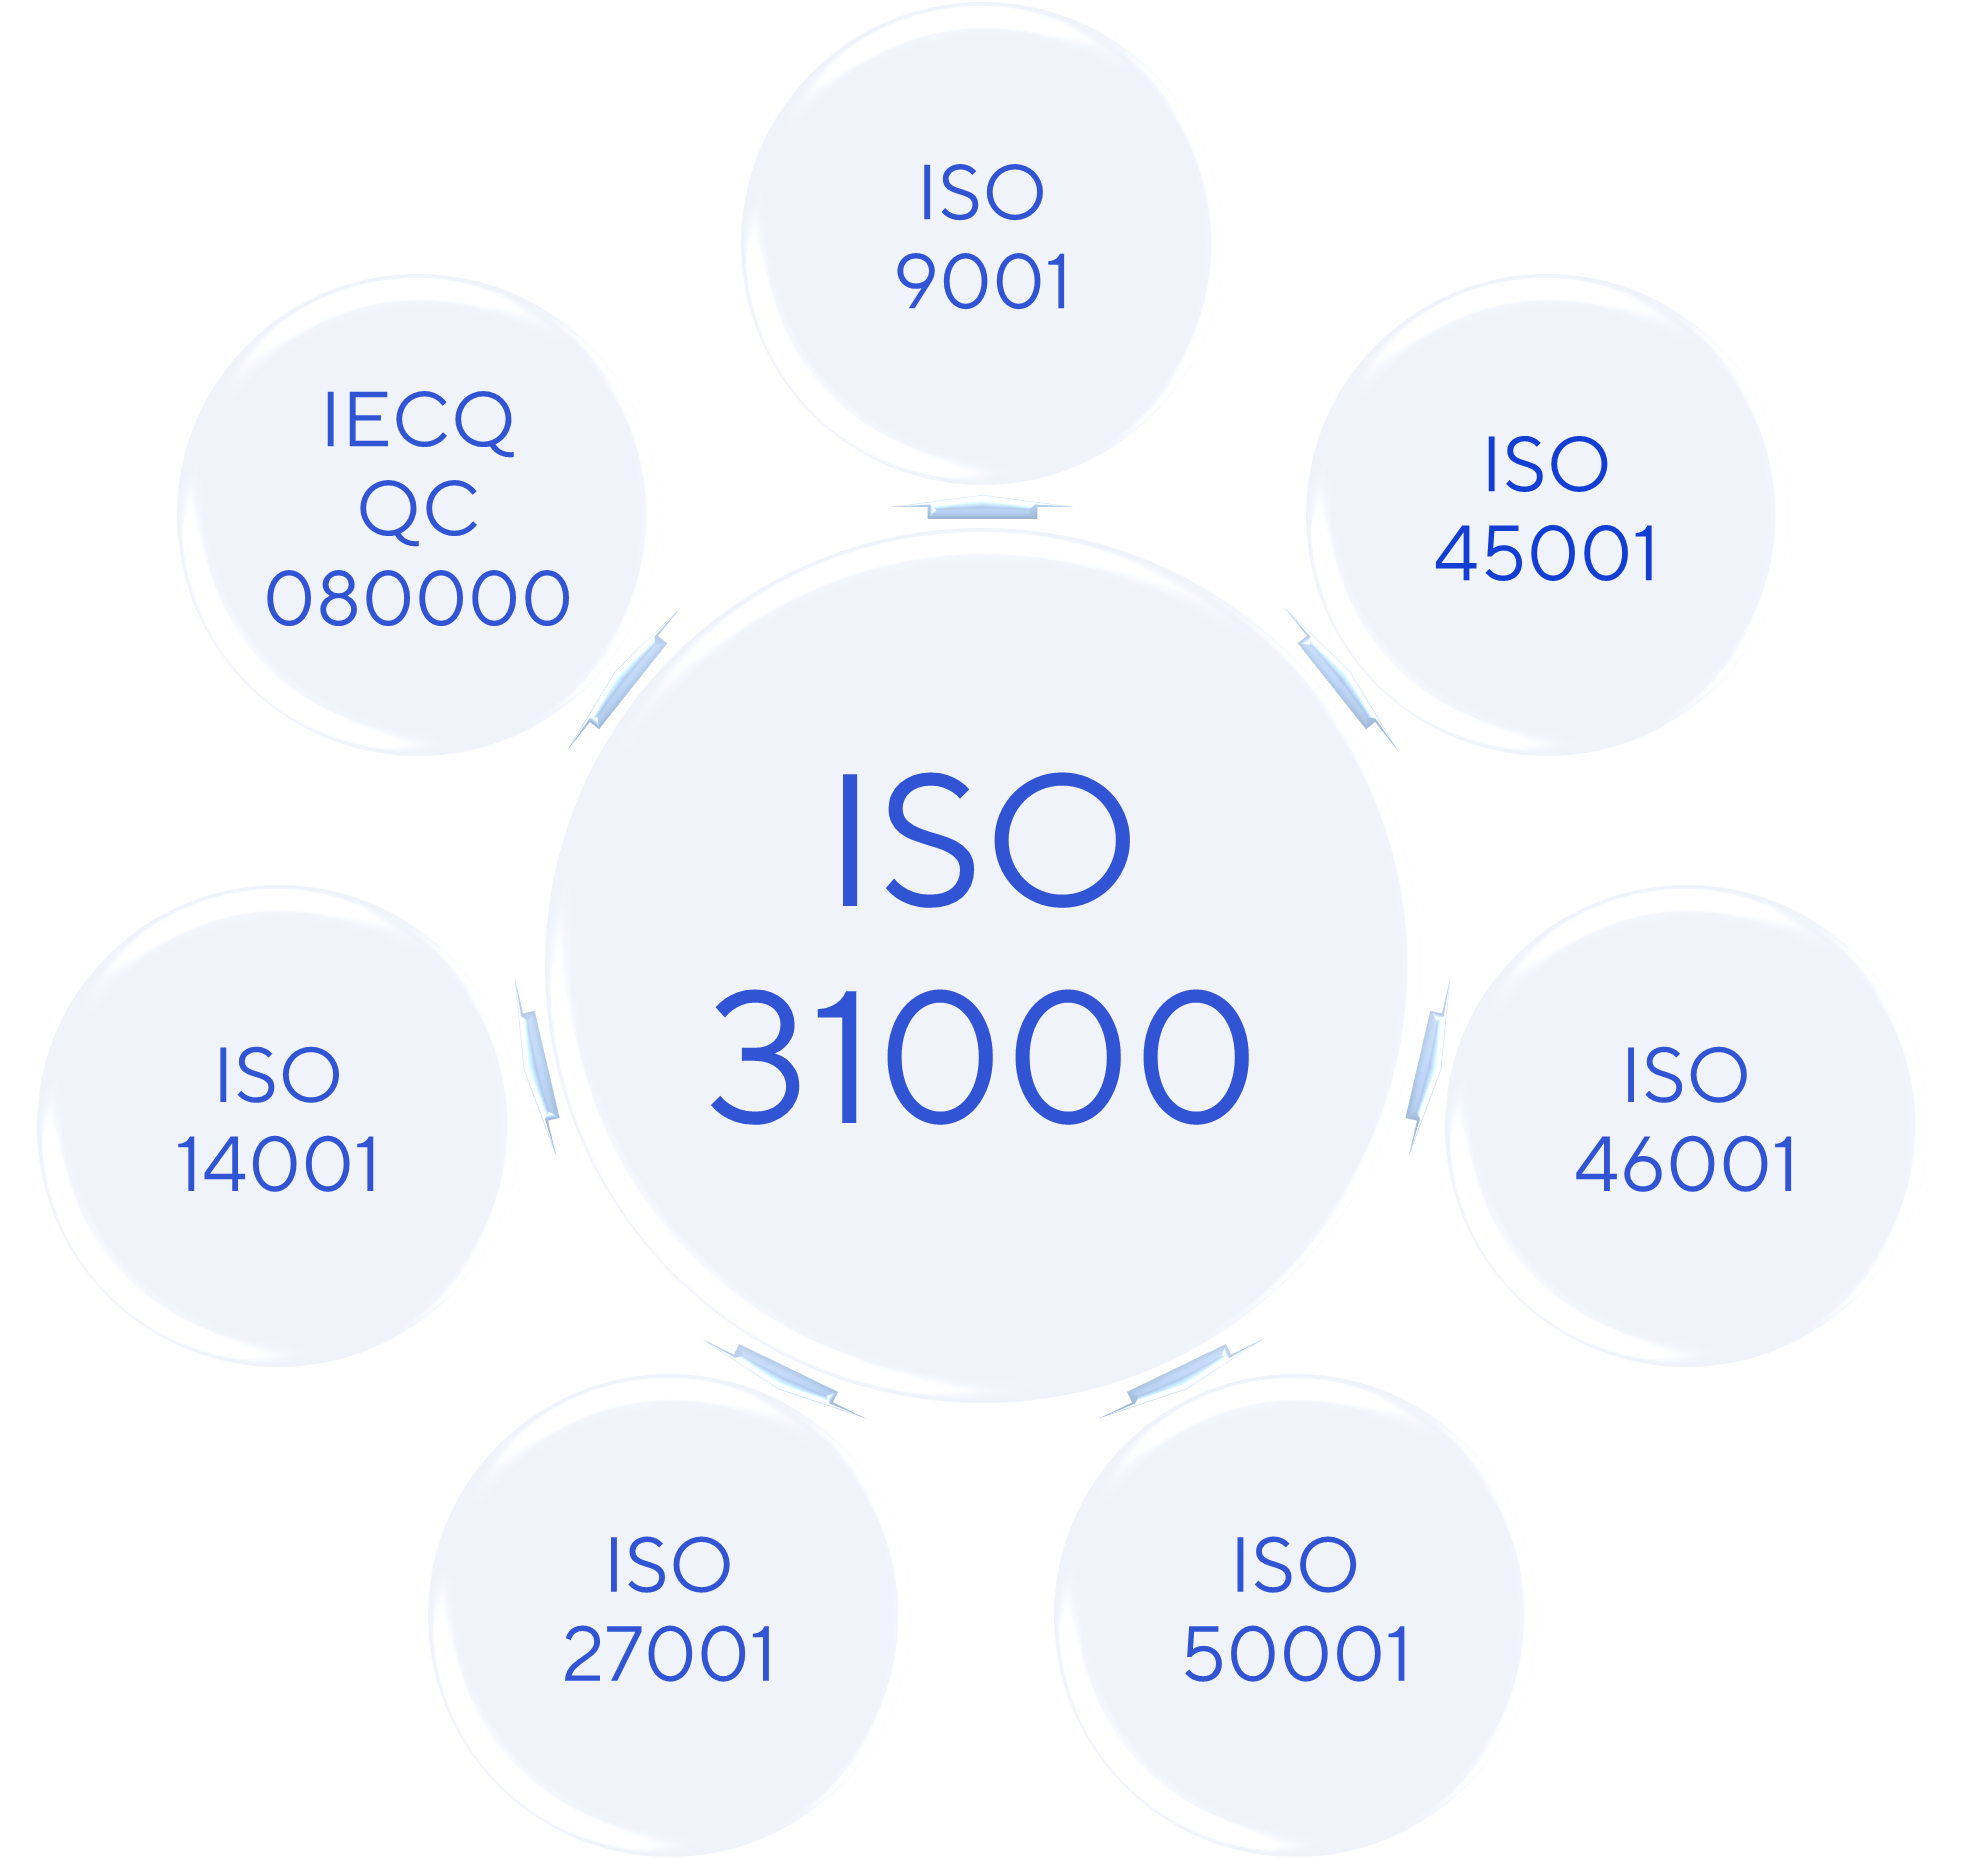
In accordance with the requirements of the ISO 31000 Risk Management System, ASUS constructs risk operations in each management system, and conducts third-party verification as well as the internal audits every year.
Enterprise Resilience
Risk Management Process
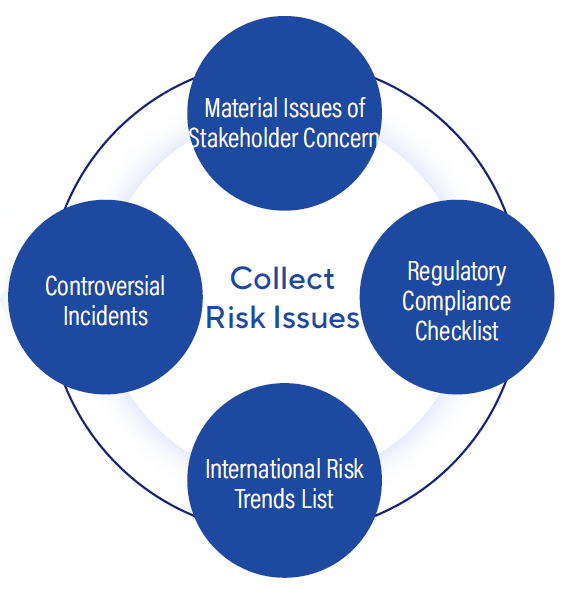
By integrating the ISO 22301 international standard for business continuity management systems with relevant tools, ASUS has developed a BCM management framework tailored to its practical needs and corporate development. The process involves collecting information from four key sources: stakeholder concerns, regulatory requirements, international risk trends, and controversial incidents. This comprehensive approach enables the identification and assessment of potential operational risks. In 2025. We established 37 Key Risk Indicators (KRIs) and risk prevention plans targeting critical resource vulnerabilities, with quarterly reviews of risk management progress; the annual KRI achievement rate reached 97%. Furthermore, beyond the existing KRIs identified by various Business Units (TUs) based on their functions, we have expanded our risk monitoring scope by introducing forwardlooking internal and external risk prevention indicators to strengthen early warning capabilities. We also leverage artificial intelligence for risk data collection, anomaly detection, and trend analysis to enhance the efficiency and depth of our risk monitoring. Through these efforts, we are gradually building intelligent risk management capabilities and extending our “All in AI” strategy to the realm of corporate management.
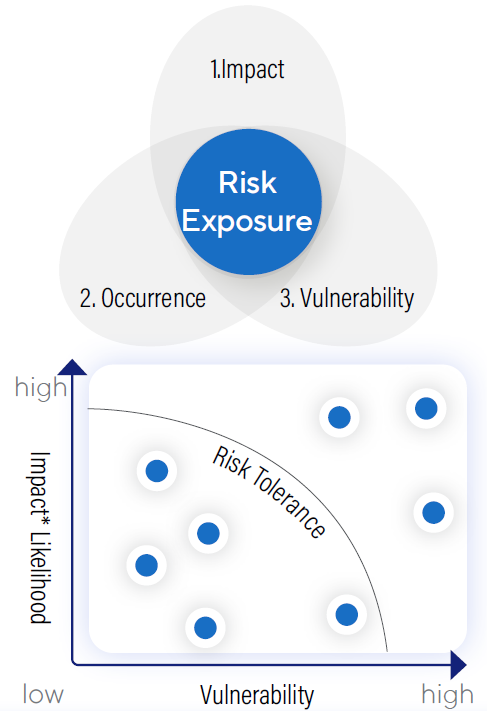
The Company conducts enterprise risk exposure reviews at least twice a year, in February and July respectively, to assess the impact of changes in the internal and external operating environment on enterprise risk. The review results serve as an important basis for reassessing major risk issues, updating the Company's risk matrix, and continuously optimizing risk management measures, ensuring that the risk management mechanism continues to respond to operational needs and changes in the external environment.
Collect
Risk Issues

Analyze
Risk Issues

Conduct
Risk Management

Regular Review and
Improvement
Major Risk Issues and Adaptation Actions
| Risk Category | Risk Issue | Potential Impact | Adaptation Actions |
|---|---|---|---|
| Technological | Escalating AI-Driven Cybersecurity Risks | AI bias, data privacy, and other ethical challenges damage corporate reputation and client trust; advanced hacker groups utilize deepfake technology and AI automation to launch attacks, exacerbating risks of information leakage and operational disruption | Implement GenAI architectural security reviews; strengthen External Attack Surface Management (EASM) monitoring and social engineering drills; deploy Cloud-Native Application Protection Platform (CNAPP) and multi-factor authentication; utilize AI-assisted threat intelligence analysis and security defense mechanisms to improve incident early warning and response efficiency |
| Societal | Talent Retention Risks due to Inclusive Workplace Gaps | Lack of understanding of employee sentiment and insufficient communication on inclusion lead to a lower sense of belonging, exacerbating talent attrition and affecting organizational stability | Regularly conduct employee engagement surveys to capture genuine sentiment; organize diversity and inclusion activities to implement inclusive practices in daily work; continuously monitor key talent turnover indicators and strengthen the analysis and application of employee experience and organizational performance |
| Societal | Damage to Brand Reputation from Corruption and Bribery | Inadequate internal controls on corporate integrity increase the risk of employee or supplier involvement in bribery, leading to litigation, fines, and restricted international investment, which damages brand reputation | Implement ISO 37001 Anti-Bribery Management System, establish policies, management manuals, and procedures; initiate risk assessments, and conduct training and due diligence for high-risk departments |
| Geopolitical | Supply Chain Restructuring Pressure from Geoeconomic Confrontation | Geopolitical conflicts necessitate local production for specific products, requiring industries to adjust supply chain planning; complex production and transaction models increase product costs and calculation difficulties | Promote supply chain diversification to disperse geographic production risks; establish real-time cost calculation mechanisms to reflect true profitability and incremental expenses; evaluate and plan supply chain scenario analysis mechanisms to enhance responsiveness to geopolitical risks |
| Economic | Macroeconomic Fluctuations and Inflationary Pressures | Changes in business, geopolitical, and economic landscapes, market demand, exchange rates, and supply chain fluctuations exacerbate inflationary pressures and drive up prices | Dynamically review products and business models, regularly analyze profitability risk changes to support management decision-making, strengthen pricing and product adjustment capabilities; implement inventory reduction and raw material hedging against market volatility to mitigate inventory valuation losses and costs |
| Environmental | Structural Compliance Gaps due to Expanding Sustainability Regulations | International sustainability regulations expand management boundaries to the entire group. Compliance gaps significantly impact the group's overall sustainability performance | Establish a Sustainability Development Committee to strengthen oversight of group-wide initiatives; focus on promoting group SBT carbon reduction targets, sustainability reporting frameworks, RBA Code of Conduct, and controversial incident management |
Emerging Risks
| Risk Category | Risk Issue | Potential Impact | Adaptation Actions |
|---|---|---|---|
| Technological | Structural Imbalance in the AI Talent Market | Concentration of core AI expertise and human resources in a few leading companies creates structural barriers. In the long term, failure to establish independent AI capability cultivation pipelines poses a continuous risk of weakening corporate innovation and operational resilience | Monitor AI talent acquisition status; expand industry-academia collaboration and diverse recruitment channels; strengthen AI talent compensation competitiveness; systematically enhance AI capabilities for all employees |
| Technological | Systemic Long-term Vulnerabilities in Digital Supply Chain Cybersecurity | As supply chain digitalization and third-party integration deepen, cybersecurity attack surfaces will expand long-term. With evolving attacker techniques and potentially unprecedented infiltration methods, this could cause unforeseen collateral damage to brand trust, legal compliance, and partnership relationships | Promote cybersecurity grading commitments for suppliers; integrate threat intelligence platforms; establish continuous External Attack Surface Management (EASM) capabilities; ensure participant authenticity and prevent unauthorized infiltration through enhanced identity verification and system controls |
| Technological | Long-term Financial Impact of GenAI Infrastructure Strategic Layout | GenAI triggers a paradigm shift in computing demand. Failure to timely adjust AI server and infrastructure layout may result in a gradual loss of market penetration opportunities. Simultaneously, as business models shift from hardware sales to integrated solutions, gross margin structures will face long-term compression pressure | Strengthen AI infrastructure technical capabilities and product portfolios; enhance solution competitiveness through cross-domain technology integration; build AI critical risk capabilities and operational resilience |
| Geopolitical | Long-term Supply Chain Restructuring Risk Triggered by Geopolitical Conflicts | Conflicts such as US-China confrontations and Red Sea crises indicate that global supply chain vulnerabilities will persist long-term. Failure to promptly establish diverse supply capabilities for critical components (High-end IC, PCB) will expose the enterprise to irreversible supply chain disruptions and financial impacts | Simulate supply disruption scenarios across multiple environments; establish logistics dispatching, inventory optimization, and cost-locking solutions; promote the diversification of critical component sourcing |
Risk Culture Development
Risk Awareness
- Continuous Risk Education and Training: Build a company-wide risk management culture through ongoing education and daily advocacy.
- Linking Risk Management Performance to Incentives: Integrate risk management deeply into corporate culture and compensation systems, establishing a dual-track mechanism of "positive incentives and negative constraints".
Group Resilience
- Multi-dimensional Dynamic Risk Monitoring: Utilize the “ASUS Group 360° Watch” mechanism to monitor group controversial incidents, covering four major dimensions: environment, business ethics, labor human rights, and sustainable procurement. Furthermore, plans are in place to introduce AI to monitor global negative sentiment regarding the group, providing real-time detection and early warnings for risks that may affect the group’s reputation, thereby enhancing response speed.
- Implementation of a Group Risk Management Mechanism: Establish a group-wide controversial incident management mechanism to be reviewed and improved by the Sustainability Committee. Integrate this with management systems, standardize improvement measures, and include them in internal audit spot checks to ensure implementation.
- Deepening Group Risk Awareness: Extend the “Controversial Incident Risk Prevention” course from the parent company to all employees across subsidiaries to improve information transparency and enhance risk prevention awareness.
Monitoring and Identifying Controversial Incidents
- Monthly detection of controversial events through ASUS Group 360° Watch Finding
Establishing Tracking and Improvement Plans
- Tracking and improvement of group-wide controversial events
- Standardization of corrective actions
Supervision and Review
- Quarterly BCM meetings to review improvement progress
- Regular audits to supervise implementation
Implementation of Prevention and Education
- Annual company-wide risk awareness training